Software Supply Chain Security
Secure Open Source, From Source to Deployment
ActiveState builds open source from source, so the components your teams use come from a source you control instead of the open internet.
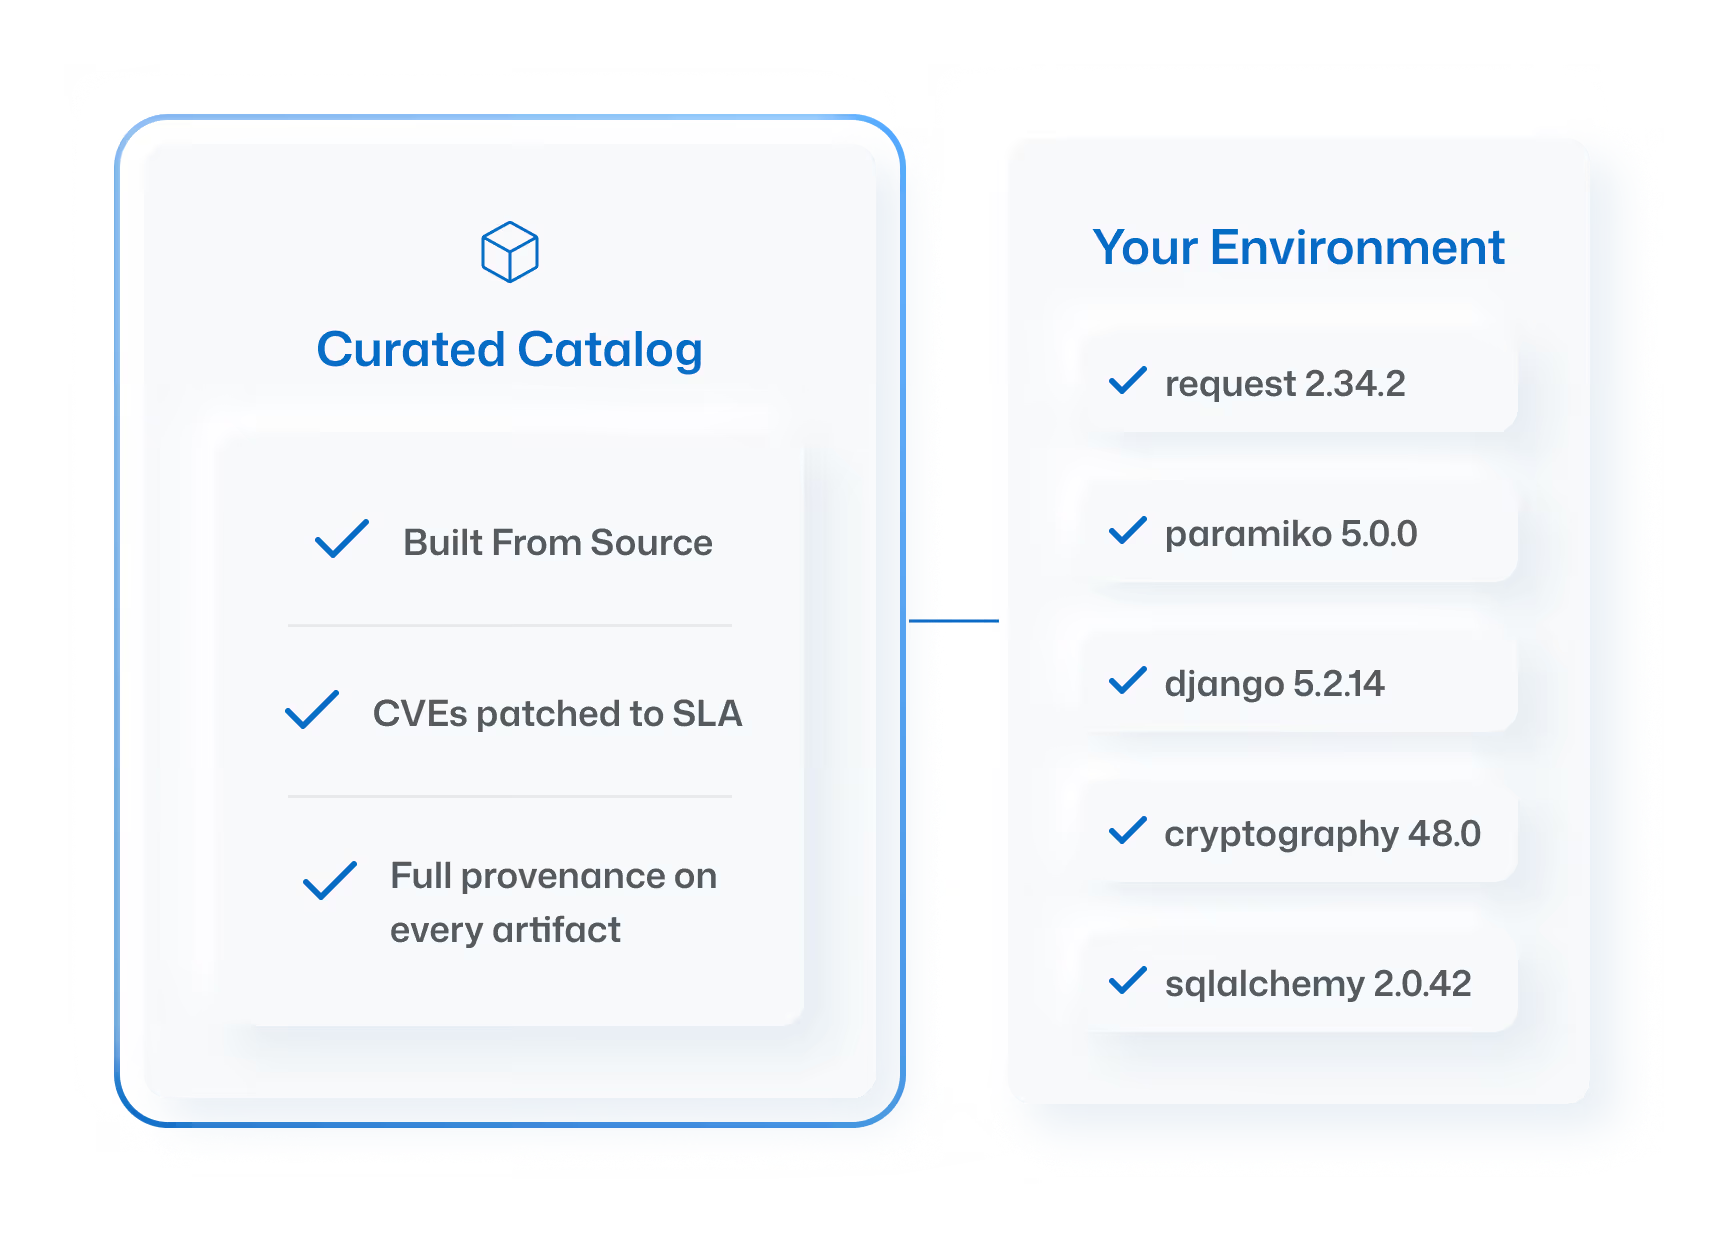
Public registries distribute risk
npm, PyPI, Maven Central, and other public registries distribute pre-compiled binaries with no guarantee of integrity. Typosquatting, dependency confusion, and malicious packages are growing attack vectors. If you're pulling directly from a public registry, you're inheriting the entire chain of custody for code you didn't write.

Built from source, with a record of where it came from
ActiveState builds open source from source. You get a clear record of where each component came from, and known malicious packages stay out of your catalog.
Built from source
Automatically generated SBOMs
Multiple language ecosystems from a single source

Governance at the catalog level
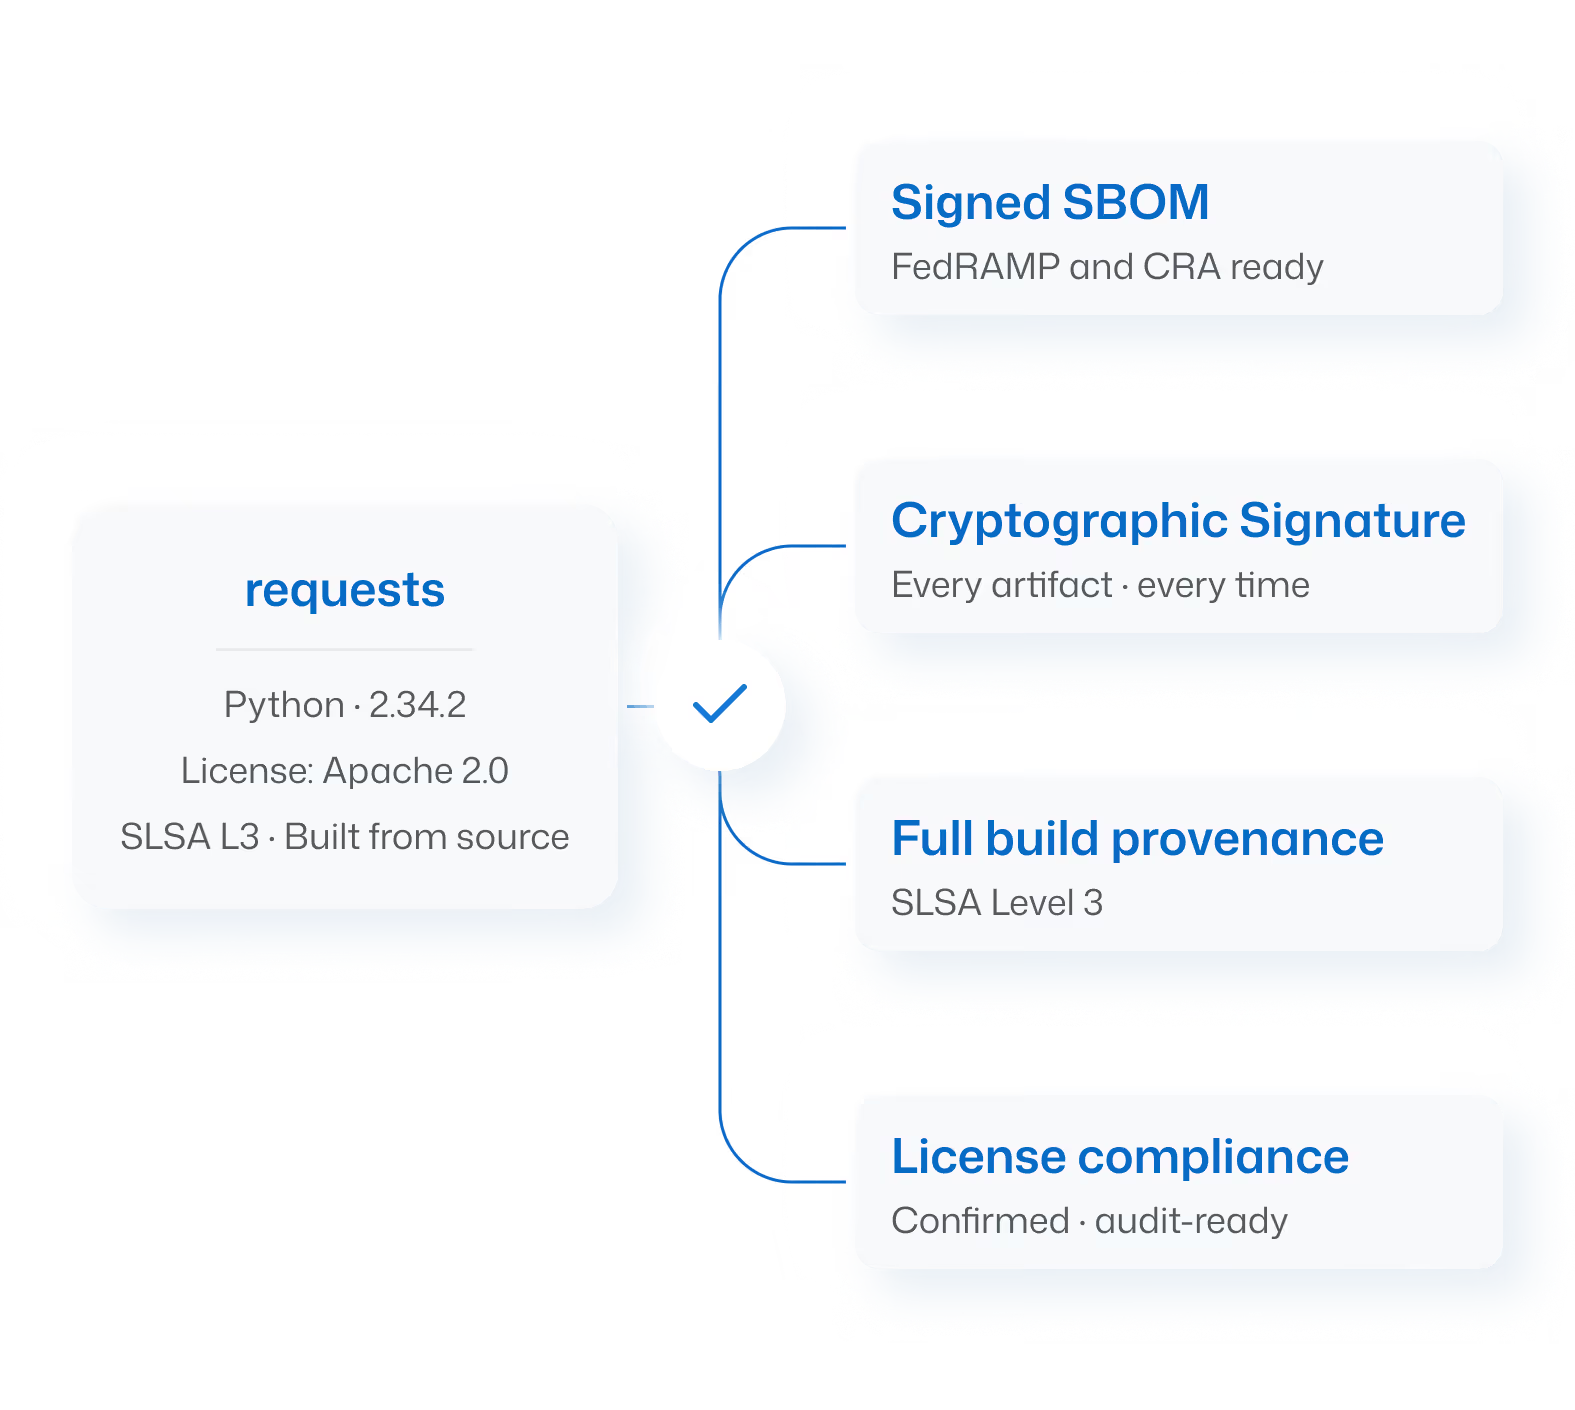
A Curated Catalog lets your organization define which components, versions, and licenses are approved. Developers pull from the catalog instead of public registries, and the dependencies AI coding assistants request resolve from the catalog too.
Approved components only, from a single source of truth
License visibility across the organization, with a system of record auditors can follow
Dependencies requested by AI coding assistants resolve from your catalog
Continuous remediation closes the loop
Provenance protects against tampering. Remediation protects against what gets disclosed next. ActiveState watches the components in your catalog and builds the fixed version from source when an upstream fix is available.
Contractual SLAs: 5 business days for critical CVEs, 10 for high, 30 for all others, from when a fix is available upstream
Daily security feed on the status of components in your catalog
90% reduction in mean time to remediation for future vulnerabilities
One managed source for your entire OSS footprint
Most organizations stitch together coverage from single-ecosystem tools. The Curated Catalog covers multiple language ecosystems, including Python, Java, and JavaScript, from one source.



Supply chain attacks prevented at the source
FAQs
Still have questions?
Talk to our team.
How does building from source improve security?
Pre-compiled packages from public registries can be tampered with between source and download. ActiveState builds open source from source, so you know where your packages came from.
Does this protect against typosquatting and dependency confusion?
Yes. Components in the Curated Catalog are verified before entering the catalog. Known malicious packages are blocked. Developers pull from a curated source instead of the open internet.
What is software supply chain security?
Software supply chain security is the practice of controlling the third-party code, mostly open source, that goes into your software, from where it comes from to how it is built and kept up to date. ActiveState secures it at the source with a private, vetted repository of open source.
Does ActiveState work alongside our existing security tools?
Yes. Keep your scanner and SCA tools; ActiveState governs what they scan. Scanners catch what's already in your code, and the Curated Catalog decides what gets in, which cuts scanner noise from false positives by about 68%.
Ready to secure your software supply chain from the source?
Contact ActiveState today to see how it works.
