Blog
Insights on securing open source from the team that builds it.
Featured posts
Open Source Is Getting Safer Upstream. Enterprises Still Choose What Gets In.
TL;DR
- OpenAI is reportedly in talks to buy Trail of Bits, its partner in patching open source upstream.
- Faster upstream patching through programs like Patch the Planet makes widely used open source projects safer for everyone.
- A merged upstream patch still has to be vetted and brought into your builds, and AI coding assistants are pulling in dependencies faster than teams can review them.
- Upstream patching makes a safe version available. Control at the source decides what gets into your software. You need both.
OpenAI's Growing Investment in Open Source Security
OpenAI is reportedly in early talks to buy Trail of Bits.1 Trail of Bits has spent years working on some of the harder problems in open source security, from vulnerability research to helping maintainers fix issues in widely used projects. The two companies are already partners.
Since June, they've run Patch the Planet, which puts OpenAI's security-focused AI models in the hands of Trail of Bits engineers. The engineers check each finding and work with maintainers of projects like cURL, Python, and Go to get patches merged.2 By mid-October, the program had flagged 1,917 issues across 67 codebases and merged 462 patches upstream.3
Nobody knows yet whether the deal will close. Either way, the work itself is good for anyone who runs open source, which is nearly everyone.
Finding Vulnerabilities Is Getting Easier. Fixing Them Isn't.
Finding a bug and getting it fixed are two very different things. A model can surface candidate vulnerabilities far faster than any team can work through them. The slow part now is everything after: reproducing the issue, ruling out false positives, writing the patch and the tests, and getting it merged by a maintainer who may be one of a handful of people on the project.
Even the public record is struggling to keep up. In April, NIST said it can no longer fully analyze every CVE submitted to the National Vulnerability Database. Submissions rose 263% between 2020 and 2025.4
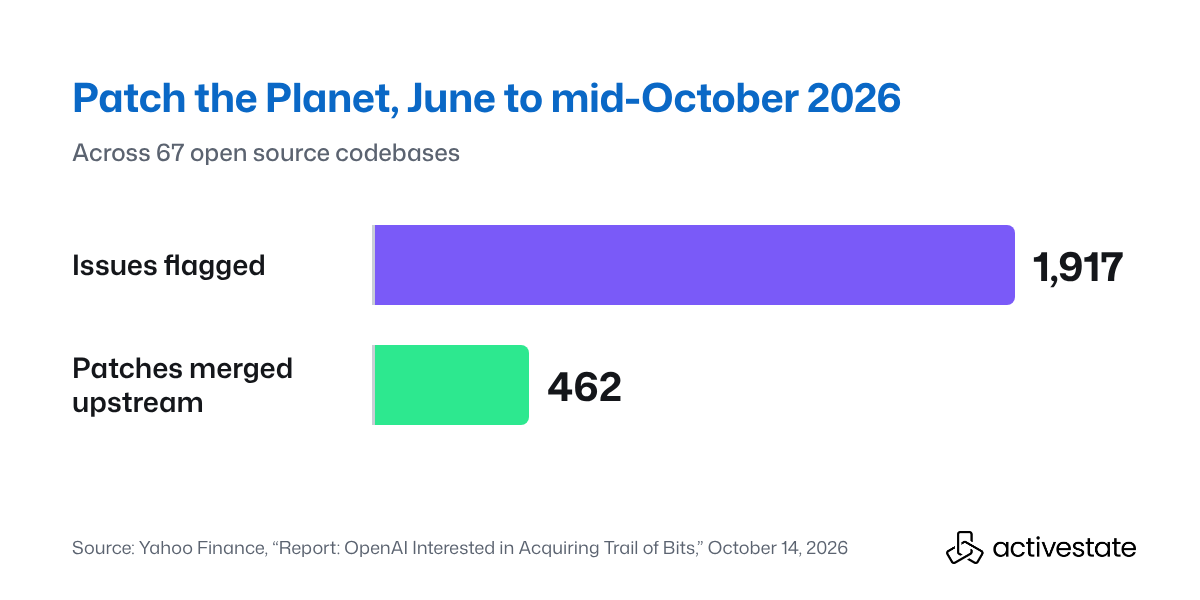
The work after discovery is what Patch the Planet was set up to handle. People review every AI finding before a maintainer ever sees it.2 Buying the team that does that work would show where OpenAI thinks the value sits now. The real investment isn't just in finding more vulnerabilities. It's in the engineering work required to validate them, develop fixes, and get those fixes accepted upstream.
An Upstream Fix Doesn't Mean You're Protected
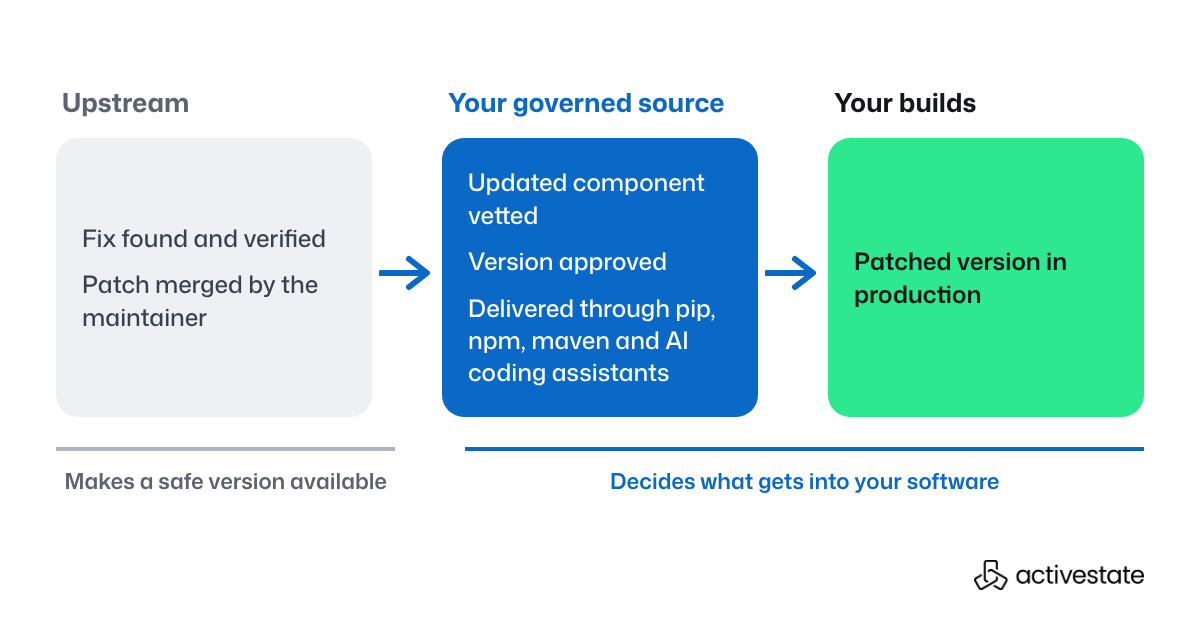
98% of applications include open source components.5 An upstream fix to an open source component doesn't automatically make its way into enterprise applications. Security and development teams still need to evaluate the updated component, approve it, and ensure the patched version is used in production builds. Remediation is already slow: industry time to remediate high and critical application vulnerabilities runs more than 50 days from detection.6
Meanwhile, AI coding assistants are changing how dependencies arrive. A developer accepts one suggestion and a whole dependency tree comes with it. A model invents a package name, and it resolves to a real package nobody vetted. ActiveState's research report, The AI Remediation Bill, found that 94% of respondents say AI has increased their open source consumption, and 63% deal with open source vulnerabilities only after a scanner finds them.7
Faster upstream patching is a welcome improvement, but enterprises still need a process for deciding which components and versions their developers and AI coding assistants can use.
Why Enterprises Still Need Dependency Controls
A security team might know that a critical Python vulnerability has been fixed upstream, but that doesn't tell them which applications still use the affected version. Nor does it prevent a developer or AI coding assistant from introducing that same vulnerable dependency into another project.
That's why faster upstream patching doesn't eliminate the need for dependency controls. Enterprises still need to decide which components and versions are approved, and control how fixes make their way into production.
Control at the source means deciding what gets into your software before developers or their AI coding assistants pull it in. Approved components and their verified dependencies come from one vetted source, through the artifact managers, native commands (pip, npm, maven), and AI coding assistants teams already use. Watch how to govern AI-generated dependencies in your development environment. Scanners stay in place as the backstop. As upstream fixes arrive faster, a governed source carries them into your builds on a clock you can plan around: ActiveState's continuous remediation brings a 90% reduction in mean time to remediation for future vulnerabilities.
Visibility tells you what entered. Control changes what gets in.
What This Means for Enterprise Security
We expect to see more investment in upstream open source security as AI makes vulnerability discovery faster and easier. That's a positive development for the entire software ecosystem.
But you can't assume those improvements will automatically translate into more secure applications. You still need to decide which dependencies get used, how quickly patched versions reach your builds, and whether developers and AI coding assistants are working from approved sources.
The goal is simple: take every upstream fix you can get, and decide for yourself what comes in.
For a closer look at what happens when organizations address these risks after the fact, read The AI Remediation Bill, based on research with 307 survey respondents.
Sources
- PYMNTS, "OpenAI Weighs Deal for One-Time Security Partner Trail of Bits," October 14, 2026, citing The Information (October 13, 2026). pymnts.com
- OpenAI, "Patch the Planet: a Daybreak initiative to support open source maintainers," June 22, 2026. openai.com
- Yahoo Finance, "Report: OpenAI Interested in Acquiring Trail of Bits," October 14, 2026. finance.yahoo.com
- NIST, "NIST Updates NVD Operations to Address Record CVE Growth," April 15, 2026. nist.gov
- Black Duck, 2026 Open Source Security and Risk Analysis Report. blackduck.com
- Edgescan, 2026 Vulnerability Statistics Report (high and critical application vulnerabilities, measured from detection). edgescan.com
- ActiveState, The AI Remediation Bill, research by Moving Horizon, September 2026 (307 survey respondents, 10 interviews; self-reported). go.activestate.com
Read the article